Enterprise Mobile Security 2026: Protecting Company Data on Employee Devices
Enterprise Mobile Security in 2026: 5 Must-Have Strategies for Protecting Company Data on Employee Devices
In an era where mobile devices are integral to business operations, safeguarding sensitive company data has become more critical than ever. As we look towards 2026, the landscape of cyber threats continues to evolve, making robust enterprise mobile security an absolute necessity. This comprehensive guide will explore five indispensable strategies that organizations must implement to protect their valuable information on employee devices.
The Evolving Threat Landscape for Enterprise Mobile Security
The proliferation of mobile devices in the workplace, fueled by bring-your-own-device (BYOD) policies and remote work trends, has blurred the lines between personal and professional usage. While this offers unparalleled flexibility and productivity, it simultaneously introduces significant security vulnerabilities. Cybercriminals are increasingly targeting mobile endpoints, recognizing them as potential gateways into corporate networks.
In 2026, we anticipate a surge in sophisticated mobile malware, phishing attacks specifically designed for mobile interfaces, and advanced persistent threats (APTs) that exploit vulnerabilities in mobile operating systems and applications. Data breaches originating from lost or stolen devices, insecure public Wi-Fi networks, and unpatched software will continue to pose substantial risks. Therefore, a proactive and multi-faceted approach to enterprise mobile security is not just recommended; it’s imperative for business continuity and data integrity.
Organizations must move beyond basic password protection and embrace comprehensive security frameworks that address the entire mobile threat surface. This includes not only the devices themselves but also the applications running on them, the networks they connect to, and the human element involved in their usage. Understanding these evolving threats is the first step towards building an resilient enterprise mobile security posture.
Strategy 1: Implementing Robust Mobile Device Management (MDM) and Unified Endpoint Management (UEM)
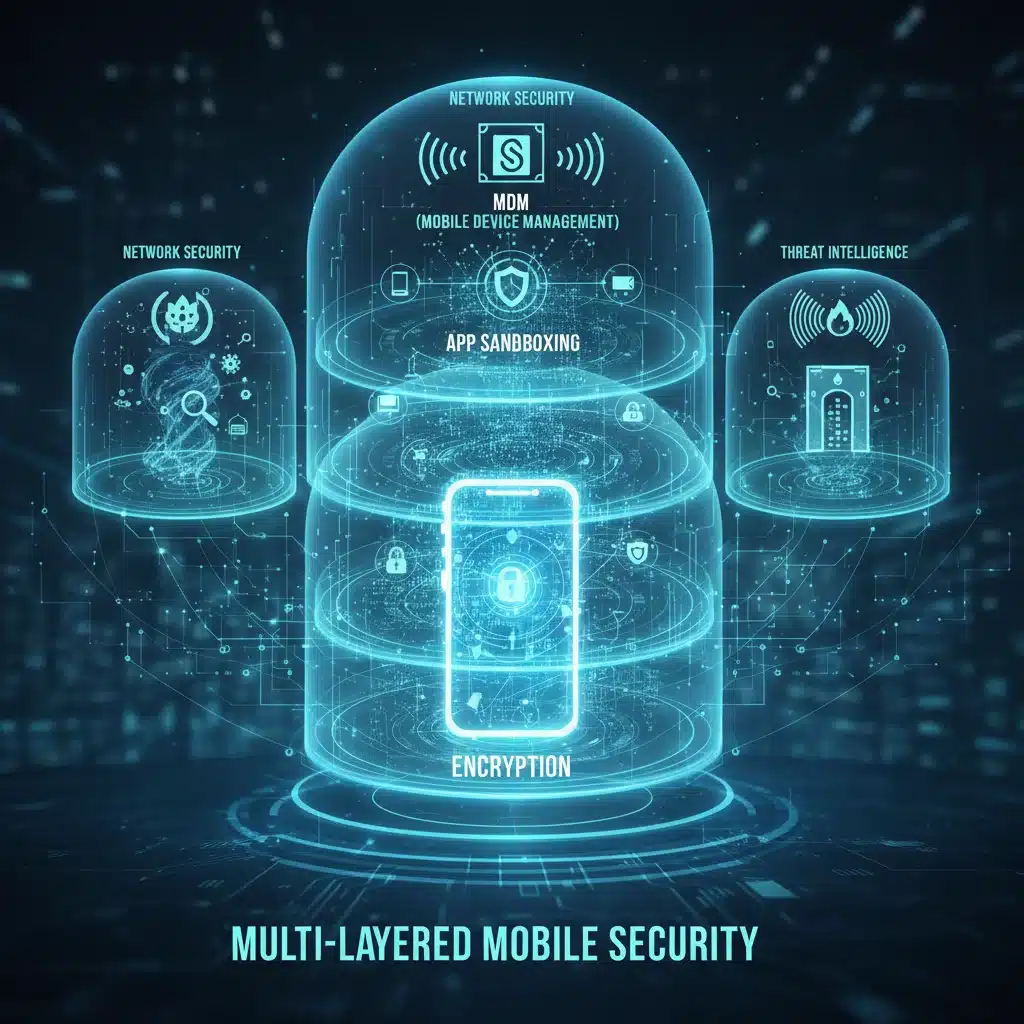
At the core of any effective enterprise mobile security strategy lies a robust Mobile Device Management (MDM) or, more comprehensively, a Unified Endpoint Management (UEM) solution. These platforms provide centralized control over all mobile devices accessing corporate resources, regardless of ownership.
An MDM/UEM solution allows IT administrators to:
- Enforce Security Policies: Automatically push and enforce security policies, such as strong password requirements, encryption settings, and screen lock durations, across all enrolled devices. This ensures a consistent security baseline.
- Remote Management: Remotely wipe, lock, or locate lost or stolen devices, preventing unauthorized access to sensitive company data. This capability is crucial for incident response.
- Application Management: Control which applications can be installed on devices, create whitelists/blacklists, and distribute approved corporate applications securely. This mitigates risks from malicious or unapproved apps.
- Configuration Management: Configure Wi-Fi, VPN, and email settings automatically, ensuring devices connect to secure networks and services.
- Inventory and Asset Tracking: Maintain an up-to-date inventory of all devices, their operating systems, and security statuses, providing crucial visibility for compliance and auditing.
By 2026, UEM solutions will be particularly vital as they extend management capabilities beyond mobile devices to include laptops, desktops, and even IoT devices, offering a holistic view of the entire endpoint landscape. This unified approach simplifies management and enhances the overall security posture, making it a cornerstone of modern enterprise mobile security.
Furthermore, an effective MDM/UEM system should integrate seamlessly with other security tools, such as identity and access management (IAM) systems and threat intelligence platforms, to provide a truly comprehensive defense. Regular audits of MDM/UEM configurations are also essential to ensure they remain aligned with evolving business needs and threat models.
Strategy 2: Zero Trust Network Access (ZTNA) for Mobile Devices
The traditional perimeter-based security model is increasingly obsolete in a mobile-first, cloud-centric world. Zero Trust Network Access (ZTNA) is emerging as a foundational principle for modern enterprise mobile security, assuming that no user, device, or application can be implicitly trusted, regardless of its location.
ZTNA for mobile devices means that every access request to corporate resources, whether from an employee’s personal smartphone or a company-issued tablet, must be explicitly verified. This involves:
- Identity Verification: Strong multi-factor authentication (MFA) is mandatory for all access attempts, verifying the user’s identity before granting access.
- Device Posture Checks: Before granting access, the device’s security posture is assessed. This includes checking for up-to-date operating systems, security patches, enabled encryption, and the absence of malware or jailbreaking/rooting.
- Least Privilege Access: Users are granted access only to the specific applications and data they need to perform their job functions, rather than broad network access.
- Continuous Monitoring: User and device behavior are continuously monitored for anomalies. Any suspicious activity triggers re-authentication or revocation of access.
Implementing ZTNA significantly reduces the attack surface for mobile devices. Even if a mobile device is compromised, the breach is contained, preventing lateral movement within the corporate network. This strategy is particularly effective for BYOD environments, where a diverse range of personal devices access corporate data. By 2026, ZTNA will be an indispensable component of any robust enterprise mobile security framework.
The shift to ZTNA requires a cultural change within organizations, emphasizing that security is a shared responsibility and that trust must always be earned. Training employees on the importance of ZTNA principles and how to report suspicious activities will be crucial for its successful adoption.
Strategy 3: Advanced Threat Protection and Data Loss Prevention (DLP) for Mobile
Beyond managing devices and controlling access, organizations must actively protect against sophisticated mobile threats and prevent sensitive data from leaving controlled environments. This calls for advanced threat protection and Data Loss Prevention (DLP) solutions tailored for mobile.
Mobile Threat Protection (MTP)
MTP solutions provide real-time protection against a wide array of mobile-specific threats, including:
- Malware and Ransomware: Detecting and neutralizing malicious applications, including those disguised as legitimate apps.
- Phishing and Smishing: Identifying and blocking phishing attempts delivered via email, SMS, or messaging apps, which are often more successful on mobile due to smaller screens and user complacency.
- Network Attacks: Protecting against man-in-the-middle attacks, insecure Wi-Fi networks, and malicious network configurations.
- OS and Application Vulnerabilities: Identifying unpatched vulnerabilities in operating systems and applications that could be exploited by attackers.
These solutions often leverage artificial intelligence (AI) and machine learning (ML) to analyze app behavior, network traffic, and device configurations, providing proactive defense against zero-day threats. Integrating MTP with MDM/UEM solutions creates a powerful, unified defense against mobile cyber threats, greatly enhancing enterprise mobile security.
Mobile Data Loss Prevention (DLP)
Mobile DLP focuses on preventing sensitive corporate data from being accidentally or maliciously exfiltrated from employee devices. Key capabilities include:
- Content Inspection: Identifying and classifying sensitive data (e.g., PII, financial records, intellectual property) on mobile devices.
- Policy Enforcement: Enforcing policies that prevent data from being copied to unapproved applications, cloud storage, or external media.
- Secure Containers: Creating secure, encrypted containers on devices to isolate corporate data from personal data, preventing data leakage.
- Auditing and Reporting: Tracking data movement and access, providing an audit trail for compliance and forensic analysis.
By combining MTP and Mobile DLP, organizations can achieve a comprehensive defense against both external attacks and internal data leakage risks, solidifying their enterprise mobile security posture for 2026 and beyond. This dual approach ensures that even if a threat bypasses initial defenses, sensitive data remains protected.
Strategy 4: Robust Employee Training and Awareness Programs
Technology alone cannot guarantee complete security. The human element remains the weakest link in many security chains. Therefore, comprehensive employee training and awareness programs are an indispensable strategy for strengthening enterprise mobile security.
These programs should be continuous, engaging, and cover a range of topics pertinent to mobile usage, including:
- Phishing and Social Engineering Awareness: Educating employees on how to identify and report phishing, smishing, and vishing attempts, which are often highly effective on mobile platforms.
- Secure Mobile Practices: Best practices for using mobile devices, such as avoiding public Wi-Fi for sensitive tasks, regularly updating operating systems and apps, and using strong, unique passwords.
- BYOD Policies: Clearly communicating the organization’s BYOD policies, including acceptable use, data handling procedures, and the implications of device enrollment in MDM/UEM.
- Reporting Incidents: Establishing clear channels and procedures for employees to report lost/stolen devices, suspicious activity, or potential security breaches promptly.
- Data Privacy and Compliance: Training on data privacy regulations (e.g., GDPR, CCPA) and how they apply to mobile data handling, ensuring employees understand their responsibilities.
Regular simulated phishing campaigns targeting mobile devices can also help reinforce training and identify areas where further education is needed. By fostering a security-aware culture, organizations can significantly reduce the risk of human error leading to security incidents, making employees an active part of the enterprise mobile security solution rather than a vulnerability.
Effective training programs should be tailored to different user groups and roles, recognizing that executives, frontline staff, and IT personnel may have varying levels of technical understanding and exposure to sensitive data. Gamification and interactive modules can also increase engagement and retention of security best practices.
Strategy 5: Regular Security Audits, Patch Management, and Incident Response Planning
Even with the most advanced security solutions in place, the threat landscape is dynamic. Continuous vigilance, regular assessments, and a well-defined incident response plan are crucial for maintaining effective enterprise mobile security.
Regular Security Audits and Assessments
Organizations should conduct periodic security audits and penetration testing specifically targeting mobile devices and applications. This includes:
- Vulnerability Assessments: Identifying weaknesses in mobile operating systems, applications, and network configurations.
- Penetration Testing: Simulating real-world attacks to test the effectiveness of existing security controls and identify potential entry points for attackers.
- Compliance Audits: Ensuring that mobile security practices align with industry regulations and internal policies.
- Risk Assessments: Regularly evaluating potential threats and their impact on mobile data, adjusting security strategies accordingly.
These assessments provide valuable insights into the organization’s security posture and help prioritize remediation efforts, ensuring that enterprise mobile security remains robust against emerging threats.
Proactive Patch Management
Unpatched vulnerabilities are a primary target for cybercriminals. A rigorous patch management strategy for mobile devices is non-negotiable. This involves:
- Timely Updates: Ensuring that mobile operating systems (iOS, Android) and all applications are updated to the latest versions as soon as patches are released.
- Automated Patching: Leveraging MDM/UEM solutions to automate the distribution and installation of security updates across all managed devices.
- Vulnerability Monitoring: Staying informed about newly discovered mobile vulnerabilities and proactively applying relevant patches.
A delay in patching can open critical windows for attackers to exploit known weaknesses, compromising enterprise mobile security.
Comprehensive Incident Response Planning
Despite best efforts, security incidents can occur. A well-defined and regularly tested incident response plan for mobile devices is essential. This plan should outline clear steps for:
- Detection and Triage: How to quickly identify and assess mobile security incidents.
- Containment: Steps to isolate compromised devices and prevent further spread of an attack (e.g., remote wipe, blocking network access).
- Eradication: Removing the threat from the affected devices and systems.
- Recovery: Restoring affected devices and data to their pre-incident state.
- Post-Incident Analysis: Learning from the incident to improve future enterprise mobile security measures.
- Communication: Protocols for internal and external communication during and after an incident.
Regular drills and tabletop exercises involving all relevant stakeholders (IT, legal, HR, communications) are crucial to ensure that the plan is effective and that teams can execute it efficiently under pressure. A prepared response minimizes damage and accelerates recovery, reinforcing the overall enterprise mobile security framework.
The Future of Enterprise Mobile Security: Beyond 2026
As we look beyond 2026, the convergence of technologies like 5G, IoT, and advanced AI will further complicate the mobile security landscape. Organizations will need to anticipate and adapt to new challenges, including:
- Edge Computing Security: Securing data and applications processed at the network edge on mobile devices.
- AI-Powered Threats: Countering sophisticated attacks generated or enhanced by artificial intelligence.
- Quantum-Resistant Cryptography: Preparing for the eventual need for cryptographic solutions that can withstand quantum computing attacks.
- Privacy-Enhancing Technologies: Balancing security needs with increasing demands for user privacy and data localization.
The strategies outlined here form a strong foundation, but continuous innovation and adaptation will be key to maintaining robust enterprise mobile security in an ever-evolving digital world. Investing in future-proof security architectures and fostering a culture of continuous learning and improvement will ensure long-term resilience.
Conclusion: Building an Unbreakable Mobile Defense
The ubiquitous nature of mobile devices makes them both a powerful asset and a significant vulnerability for enterprises. As we approach 2026, the imperative to implement comprehensive enterprise mobile security strategies has never been clearer. By focusing on robust MDM/UEM, adopting Zero Trust principles, deploying advanced threat protection and DLP, investing in continuous employee training, and maintaining rigorous audit and incident response plans, organizations can build an unbreakable mobile defense.
Protecting company data on employee devices is not merely a technical challenge; it’s a strategic business imperative that safeguards intellectual property, maintains customer trust, ensures regulatory compliance, and preserves brand reputation. Proactive and adaptive security measures will define the successful enterprise in the mobile-first future. Embrace these strategies today to secure your digital tomorrow.